Staff and users
The two families and nine exposure categories: what each one holds, why they do not weigh the same, and how they drive the cockpit, the filters, the score and the alerts.
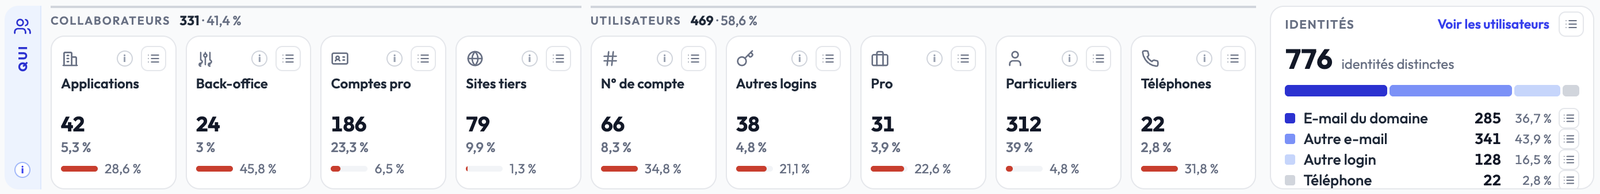
Every credential Stealed detects is classified automatically into exactly one of nine categories, based on two things: its login (e-mail, number, nickname...) and the site it is used on. The categories fall into two families:
- Staff: the credentials of the people of your organisation, with an e-mail of your domain or access to your back-office.
- Users: the credentials of the people who use your sites, with a login that is not an e-mail of your domain.
Why it matters
A stolen back-office login does not weigh like a customer's personal account. The first opens a door into your information system and calls for immediate action: reset the access, check the sessions, examine the infected machine. The second exposes a customer to account takeover on your service: it calls for a password reset, MFA enforcement or customer notification.
Categories keep these cases apart so you handle what matters first, and a large volume of customer accounts never hides a single compromised internal access.
Staff
| Category | Short label | What it holds | Example |
|---|---|---|---|
| Internal applications | Applications | An e-mail of the organisation's domain, used on one of its sites. | [email protected] on hr.acme.com |
| Internal access and back-office | Back-office | Another login, without a domain e-mail, on a staff access portal (web mail such as OWA, single sign-on such as ADFS, remote access such as Citrix, intranet) or on an administration page of one of the organisation's sites. | admin on the administration page of www.acme.com |
| Enterprise accounts | Pro accounts | A domain e-mail on an identity platform or an enterprise tool (mail, SSO, collaboration tools). | [email protected] on an online mail service |
| Third-party sites | Third-party | A domain e-mail on any other site. | [email protected] on an e-commerce site |
Users
Users categories all apply to the organisation's sites, outside administration pages.
| Category | Short label | What it holds | Example |
|---|---|---|---|
| Account numbers | Account no. | A login made of digits only: account, contract or subscriber number. | 00412345 on client.acme.com |
| Other logins | Other logins | A login that is neither an e-mail, nor a phone number, nor digits only: nickname, first.last without a domain, alphanumeric identifier. | jmartin75 on client.acme.com |
| Business users | Business | An e-mail of another organisation. | [email protected] on client.acme.com |
| Personal users | Personal | An e-mail from a public provider (Gmail, Orange, Free...). | [email protected] on client.acme.com |
| Phone numbers | Phones | A phone number used as login. | 0600000000 on client.acme.com |
Short labels are the ones used on the cockpit cards and in the alert form filters. In the app, the information icon of each card recalls its definition.
What categories drive
- The cockpit. The Who block shows one card per category: number of credentials, share of the total, infostealer share. See Cockpit.
- The filters. A click on a card adds the
Category: ...filter; the whole screen is recomputed, and the leak list shows the category of every row. - The score. The floors of the exposure score rely on categories: an infected employee machine weighs more than any volume of customer accounts.
- The alerts. A monitor is defined by category: for example, get alerted on every new infostealer credential in Applications, Back-office and Pro accounts. See Create a monitor.
The detailed menu pages
The detailed pages are still available in the menu:
- Internal Insight: credentials whose e-mail is on your domains.
- External Insight: credentials whose target site is on your domains.
- Keyword Insight: credentials on the sites found by your keywords.
The cockpit and its categories are now the main entry point. The menu pages slice the same data another way: one credential can appear in the first two (an e-mail of your domain used on one of your sites), while it belongs to a single category.
What's next
- Cockpit: read and filter your organisation's exposure.
- Reading detected leaks: the leak list, the leak sheet, the export.
- Create a monitor: one alert per category.